Chicago IT Support & Cyber Security | Forward Technologies

Chicago-based Forward Technologies delivers IT support and cyber security to businesses in the Chicago area and nationwide.

  • Home
  • Services
    • Outsourced IT Support
    • DMARC Email Security
    • Development
      • Web Development & Facelifts
      • CustomView: Plugin for WordPress
    • Data Recovery Service
    • PPC Marketing Services
    • SEO Services
  • Email Security
    • SPF Basics
    • DKIM Basics
    • DMARC Basics
    • Email Security Consulting
  • Data Recovery Service
  • Blog
  • Contact Us

We Finally Got Everyone Using MFA. Now It’s Changing

October 2, 2026 by Edward Silha

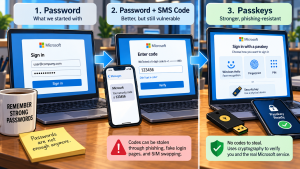
A clean cartoon showing the evolution of Microsoft authentication from password, to password plus SMS code, to a passkey using Windows Hello with fingerprint, face, or PIN authentication.For years, the security advice was simple: turn on multifactor authentication.

IT people repeated it endlessly. Microsoft pushed it. Insurance companies started requiring it. Cybersecurity audits looked for it. Eventually, most businesses got the message.

Users learned the routine. Enter the password. Wait for the text message. Type in the 6-digit code. Get back to work.

Now Microsoft is changing all of that. [Read more…]
Filed Under: Blog, Cybersecurity Tagged With: credential theft, cybersecurity, FIDO2, identity security, MFA, Microsoft, Microsoft 365, Microsoft 365 security, Microsoft Authenticator, Microsoft Entra, Microsoft Entra ID, Multifactor Authentication, passkeys, passwordless authentication, phishing, phishing-resistant MFA, QR code phishing, small business security, SMS Authentication, voice authentication, Windows Hello

HalluSquatting Shows Why AI Agents Still Can’t Be Trusted on Their Own

July 8, 2026 by Edward Silha

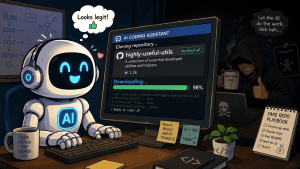
A cartoon AI coding assistant enthusiastically downloading code from a repository with a convincing but fake name while a hooded hacker quietly celebrates in the background.I’ve said from the beginning that the biggest risk with AI isn’t that it writes bad code. It’s that people are starting to trust it to make decisions it has no business making.
New research drives that point home.

Researchers have uncovered a new attack called HalluSquatting, and it exploits one of AI’s most well-known weaknesses: it would rather make something up than admit it doesn’t know the answer.

That behavior, which we’ve all come to know as hallucination, is no longer just an annoyance. It can now be turned into a weapon.

Here’s how it works. [Read more…]

Filed Under: AI, Blog, Cybersecurity Tagged With: AI hallucinations, AI security, artificial intelligence, botnets, Cline, Cursor AI, cybersecurity, developer tools, Gemini CLI, GitHub, GitHub Copilot, HalluSquatting, large language models, LLMs, malware, prompt injection, ransomware, reverse shell, secure coding, software repositories, software supply chain, typosquatting, Windsurf

Hackers Are Now Using Microsoft Teams to Break Into Corporate Networks

May 14, 2026 by Edward Silha

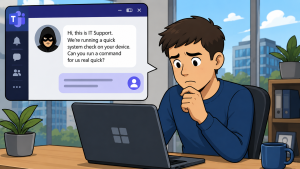
Microsoft Teams Phishing Attacks Target Corporate NetworksFor years, companies drilled one thing into employees’ heads: don’t trust weird emails. Problem is, attackers adapted. Instead of fighting against people’s skepticism around email, they moved to platforms employees already trust without thinking twice about it. One of the biggest targets right now is Microsoft Teams
A threat group called KongTuke has been using Teams chats to get inside corporate networks, and honestly, it’s working disturbingly well. Instead of blasting out phishing emails, they pose as internal IT staff and message employees directly through Teams. Sometimes they’re operating from already-compromised Microsoft 365 accounts. Other times they create fake accounts designed to look close enough to pass a quick glance. Either way, the attack can go from first contact to compromised system in just a few minutes. [Read more…]

Filed Under: Cybersecurity, Tech In General Tagged With: corporate cybersecurity, cybersecurity, enterprise security, initial access brokers, KongTuke, malware, Microsoft 365, Microsoft 365 security, Microsoft Teams, ModeloRAT, phishing, PowerShell attacks, ransomware, social engineering, Teams phishing, Windows security

Microsoft Eliminates SharePoint Email Passcodes, Forcing Move to Entra Guest Accounts

March 13, 2026 by Edward Silha

Cartoon illustration of Microsoft SharePoint file sharing changing from email passcodes to Microsoft Entra guest accounts for external access.Microsoft is retiring the email passcode system long used to grant temporary access to shared files in SharePoint Online and OneDrive for Business. The company plans to replace it with Microsoft Entra B2B guest accounts, shifting external collaboration toward a fully identity-based model across Microsoft 365.

The change affects both commercial and government cloud environments. Beginning in May 2026, new external sharing invitations will start using Entra B2B instead of the existing one-time passcode system. The transition will accelerate through the summer, with the older authentication method beginning its shutdown in July and disappearing completely by the end of August 2026. [Read more…]

Filed Under: Blog, Cybersecurity, Tech In General Tagged With: Conditional Access, Entra B2B, external sharing, guest accounts, identity management, Microsoft, Microsoft 365 security, Microsoft Entra, OneDrive for Business, SharePoint Online

Microsoft Adds Passkey Sign-Ins to Windows, Expanding Phishing-Resistant Authentication

March 11, 2026 by Edward Silha

Microsoft Windows login screen using passkey authentication through Microsoft Entra with Windows Hello biometric sign-in.Microsoft is expanding passwordless security across Windows by introducing passkey authentication through Microsoft Entra. The new capability allows users to sign in to Entra-protected resources using Windows Hello instead of traditional passwords, adding stronger resistance against phishing attacks and credential theft.

The feature will roll out as an opt-in public preview starting in mid-March 2026 and continuing through late April for global Microsoft 365 tenants. Government cloud environments will receive the preview shortly after, with deployments scheduled between mid-April and mid-May. Once enabled, the update allows organizations to adopt passkeys as an authentication method on Windows devices. [Read more…]

Filed Under: Blog, Cybersecurity, Tech In General Tagged With: FIDO2, identity security, Microsoft, Microsoft 365 security, Microsoft Entra, passkeys, passwordless authentication, phishing resistance, Windows authentication, Windows Hello

  • 1
  • 2
  • 3
  • …
  • 6
  • Next Page »

Social Media

  • Facebook
  • GitHub
  • LinkedIn
  • Periscope
  • Twitter

Forward Technologies
747 N LaSalle
STE 500B
Chicago, IL 60654
(312) 715-7806

Copyright © 2026 — Forward Technologies • All rights reserved. • Privacy Policy •