Chicago IT Support & Cyber Security | Forward Technologies

Chicago-based Forward Technologies delivers IT support and cyber security to businesses in the Chicago area and nationwide.

  • Home
  • Services
    • Outsourced IT Support
    • DMARC Email Security
    • Development
      • Web Development & Facelifts
      • CustomView: Plugin for WordPress
    • Data Recovery Service
    • PPC Marketing Services
    • SEO Services
  • Email Security
    • SPF Basics
    • DKIM Basics
    • DMARC Basics
    • Email Security Consulting
  • Data Recovery Service
  • Blog
  • Contact Us

Fully Patched, Still Vulnerable: The Windows Secure Boot Problem

November 3, 2026 by Edward Silha

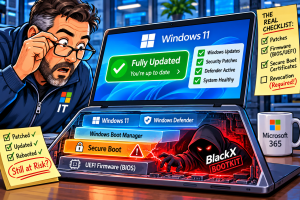
A dramatic but playful cartoon showing a Windows computer proudly displaying a green “Fully Updated” checkmark while a sneaky BlackX bootkit slips underneath the operating system through a glowing red vulnerability in the Secure Boot foundation. An IT administrator looks shocked as the supposedly protected machine reveals a hidden security weakness.For years, one of the simplest rules in IT security has been to keep systems patched.

Install the updates. Reboot when required. Make sure Windows Update is current. Move on.

That advice still holds true, but a new Windows bootkit called BlackX is a reminder that “fully patched” doesn’t always mean fully protected. [Read more…]
Filed Under: Blog, Cybersecurity Tagged With: Baton Drop, BIOS updates, BlackLotus, BlackX, bootkit, CVE-2022-21894, cybersecurity, endpoint protection, firmware security, malware persistence, Microsoft, Microsoft security, patch management, Secure Boot, Secure Boot certificates, UEFI, vulnerability management, Windows 11, Windows boot manager, Windows security, Windows Server, windows update

Microsoft Plugs One Secure Boot Flaw While Leaving Another Wide Open

June 11, 2025 by Edward Silha

A cartoon-style illustration of a worried programmer sitting at a desk with a laptop that has a red padlock icon. Behind him, a menacing robot labeled "VULNERABILITIES" holds two scrolls marked "EXPLOIT." A yellow "SECURE BOOT" sign with a padlock and boot icon hangs on the wall, symbolizing compromised device security. The background is a textured purple.Security researchers have identified two major exploits in the Secure Boot system, both capable of sidestepping one of the most important protections on modern PCs. Microsoft has issued a patch for one of them. The other remains untouched, even as it offers attackers a nearly universal method to bypass security during the startup process.

This week’s patch from Microsoft addresses a vulnerability known as CVE-2025-3052. It impacts over 50 manufacturers whose systems rely on Linux modules to support boot processes. The flaw allows someone with physical access to a device to disable Secure Boot entirely. Once that’s done, they can install malware that loads before the operating system starts. The attack is particularly concerning because it’s stealthy and persistent, and in cases where a hacker already has administrative access, it can be triggered remotely. [Read more…]

Filed Under: Blog, Cybersecurity Tagged With: Binarly, bootloader exploit, CVE-2025-3052, CVE-2025-47827, cybersecurity, DBX blocklist, digital signatures, DT Research, Eclypsium, firmware security, GRUB, IGEL, Linux kernel, malware, Microsoft, operating system security, Secure Boot, UEFI

Social Media

  • Facebook
  • GitHub
  • LinkedIn
  • Periscope
  • Twitter

Forward Technologies
747 N LaSalle
STE 500B
Chicago, IL 60654
(312) 715-7806

Copyright © 2026 — Forward Technologies • All rights reserved. • Privacy Policy •